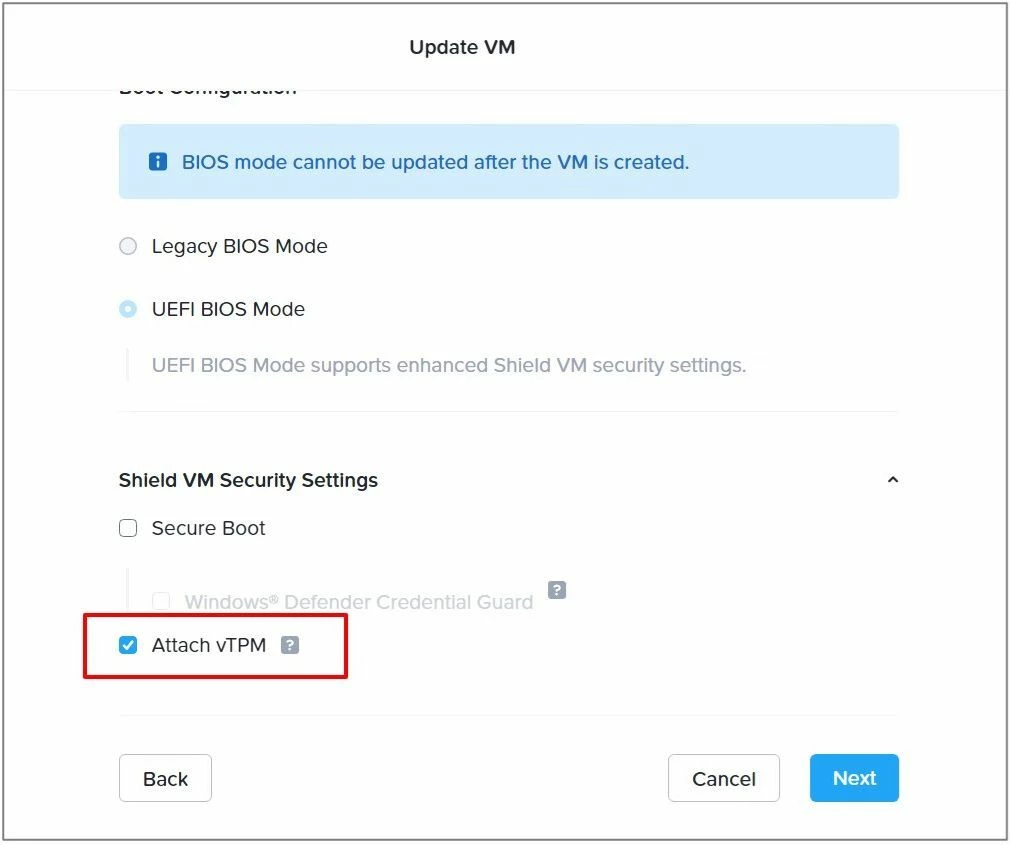

What’s a vTPM?
- The vTPM module is the virtual equivalent of a physical TPM chip.
- It securely stores cryptographic keys used for BitLocker drive encryption, Windows Secure Boot, measured boot, and attestation features.
- Each vTPM holds unique cryptographic material, and without those keys, a VM may not be able to decrypt its disks or boot securely.
Why Does Protection Domain (PD)-Based DR Fail with vTPM VMs?
- Legacy Protection Domains were built before vTPM was introduced, so PDs replicate only VM disks and metadata, not the vTPM device or its secure state.
- vTPM keys are encrypted and tied to the local cluster’s KMS.
- During PD-based replication, those keys cannot be transferred to the DR site.
- As a result, a vTPM-enabled VM may fail to boot or lose access to encrypted volumes after DR failover.
Why Does Protection Policy (PP)-Based DR Support vTPM VMs?
- Modern Protection Policy-based DR introduces full vTPM awareness.
- It replicates vTPM state and keys alongside VM data.
- It integrates with Nutanix KMS or an external KMS to ensure key availability at the DR site.
- It ensures that after failover, the vTPM device and its associated secure keys are restored correctly, allowing the VM to boot securely.