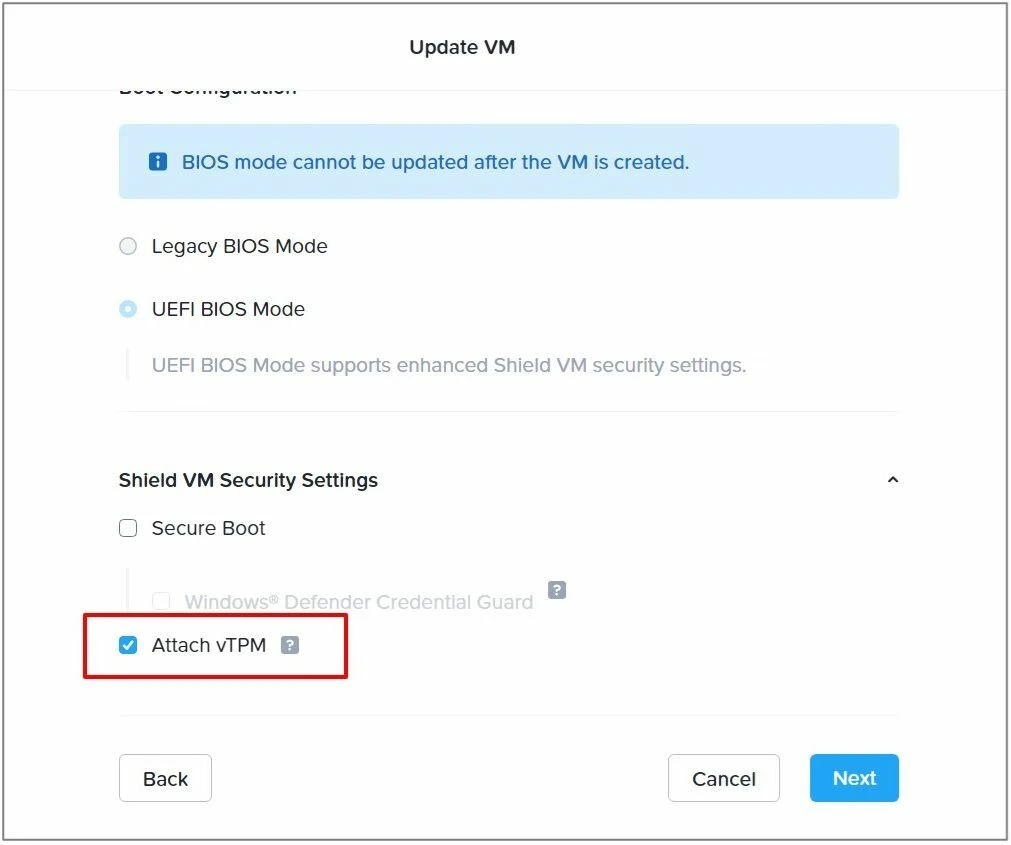

𝐖𝐡𝐚𝐭’𝐬 𝐚 𝐯𝐓𝐏𝐌?
- The vTPM module is the virtual equivalent of a physical TPM chip.
- It securely stores cryptographic keys used for BitLocker drive encryption, Windows Secure Boot, measured boot & attestation features.
- Each vTPM holds unique cryptographic material, and without those keys, a VM may not decrypt its disks or boot securely.
𝐖𝐡𝐲 𝐝𝐨𝐞𝐬 𝐏𝐫𝐨𝐭𝐞𝐜𝐭𝐢𝐨𝐧 𝐃𝐨𝐦𝐚𝐢𝐧 (𝐏𝐃)-𝐛𝐚𝐬𝐞𝐝 𝐃𝐑 𝐟𝐚𝐢𝐥 𝐰𝐢𝐭𝐡 𝐯𝐓𝐏𝐌 𝐕𝐌𝐬?
- Legacy Protection Domains were built before vTPM was introduced, so PDs replicate only VM disks + metadata, not the vTPM device or its secure state.
- vTPM keys are encrypted and tied to the local cluster’s KMS.
- During PD-based replication, those keys cannot be transferred to the DR site.
- As a result, a vTPM-enabled VM fails to boot or loses access to encrypted volumes after DR failover.
𝐖𝐡𝐲 𝐝𝐨𝐞𝐬 𝐏𝐫𝐨𝐭𝐞𝐜𝐭𝐢𝐨𝐧 𝐏𝐨𝐥𝐢𝐜𝐲 (𝐏𝐏)-𝐛𝐚𝐬𝐞𝐝 𝐃𝐑 𝐬𝐮𝐩𝐩𝐨𝐫𝐭 𝐯𝐓𝐏𝐌 𝐕𝐌𝐬?
- Modern Protection Policy-based DR introduces full vTPM awareness.
- Replicates vTPM state + keys alongside VM data.
- Integrates with Nutanix KMS or external KMS to ensure key availability at the DR site
- Ensures that after failover, the vTPM device and its associated secure keys are restored correctly, allowing the VM to boot securely.